

Google Patches Critical Zero-Click Vulnerability CVE-2026-58704 in Pixel Phones
Security Flaw in Pixel Smartphones
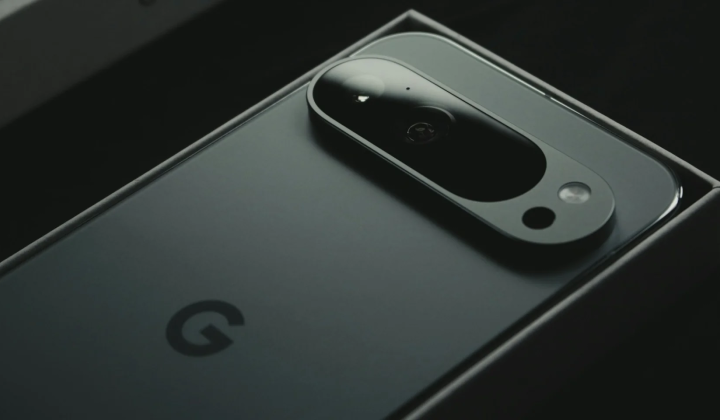
According to НВ — Техно: Google has addressed a serious vulnerability identified as CVE-2026-58704 affecting its Pixel smartphone line. This flaw was exploited in a series of targeted cyberattacks, enabling hackers to access device data without any interaction from the user, a method known as a zero-click attack. The weakness was located within the Pixel’s modem, the component responsible for connecting the device to the internet.
Threats and Guidance for Users
The modem operates inside a secure, isolated environment called a 'sandbox.' However, attackers managed to break out of this containment, allowing them to reach other sensitive information on the phone. Vulnerabilities like this are frequently leveraged by spyware developers who market their tools to governments and law enforcement agencies. Google has not disclosed the identities behind these attacks. Details about this security issue and its exploitation were reported by TechCrunch.
This incident highlights the critical importance of mobile device security, as attackers can exploit such weaknesses to harvest private data without user awareness. Pixel phone owners are strongly encouraged to update their devices promptly to safeguard their information and mitigate potential risks. Promptly addressing vulnerabilities like this is essential for maintaining user trust in Google’s products.
In light of recent vulnerabilities, it's crucial to remain vigilant about mobile security. A significant rise in malicious activities has been reported, with a threefold increase in harmful push notifications on Android devices over the past few months. This trend underscores the need for users to stay informed and proactive in protecting their personal information from emerging threats.

Read also